Enable ASUS Secure Boot for Windows 11 and Verify the Result
Secure Boot checks trusted startup software before Windows loads. On ASUS computers, the menu names vary between motherboards and laptops, so an option shown in one screenshot may not exist on another model.
Before changing firmware settings, confirm how the current Windows installation starts and make the BitLocker recovery key available. Turning off legacy boot on an MBR installation can prevent that installation from starting.
Check Windows and recovery prerequisites
- Press Windows + R, run
msinfo32, and record BIOS Mode and Secure Boot State. - If BIOS Mode is UEFI and Secure Boot State is On, the feature is already active. Investigate any remaining compatibility warning separately.
- If BIOS Mode is Legacy, inspect the Windows disk's partition style in Disk Management before disabling CSM. Plan a supported conversion or installation route first.
- Save the BitLocker recovery key outside the PC and confirm that you know the account password. Follow the device's documented encryption precautions.
- Record the exact ASUS model and current firmware version. Use its support instructions, not another model's menu sequence.
Back up files before changing the boot configuration
A separate file backup provides a recovery copy if later installation or conversion work becomes necessary. It does not replace the BitLocker key or automatically undo a firmware setting.
Step 1. Connect external storage, open Qiling Disk Master, and select File backup.
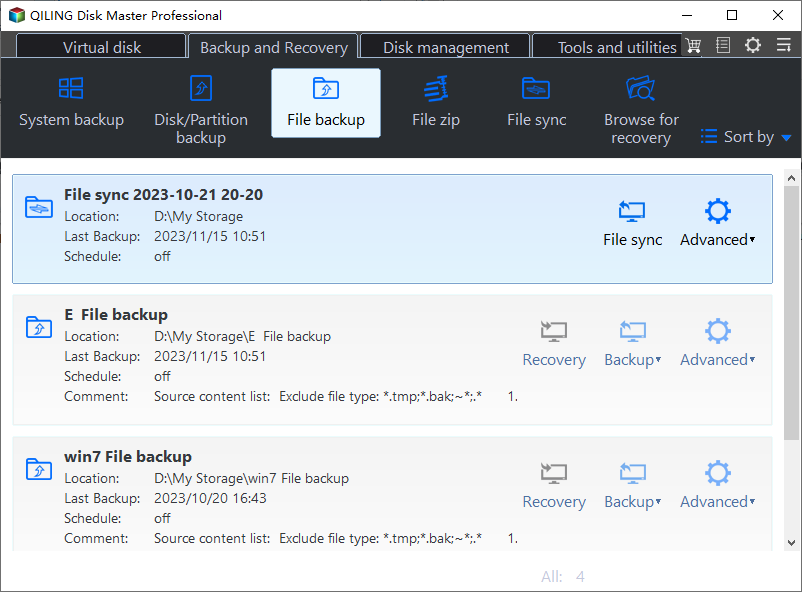
Step 2. Select your documents and work folders in the tree control. Include any files you will need if Windows cannot start after a setting change.
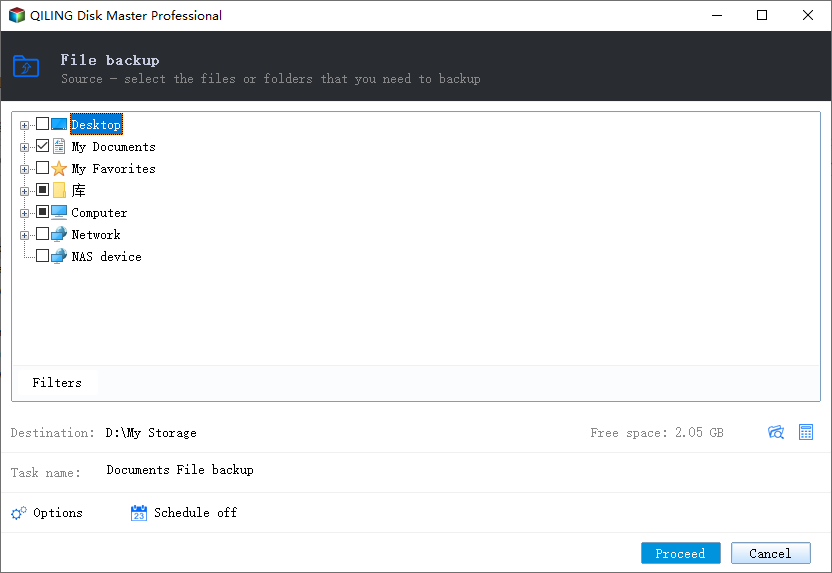
Step 3. Choose the external disk, check the task, and click Proceed. Verify a sample restore and disconnect the backup drive before entering firmware setup.
Enable Secure Boot using the model's firmware controls
The exact menu must follow the model's manual. ASUS provides separate motherboard and notebook instructions; its motherboard Secure Boot guide is a useful reference for supported boards.
- Restart into firmware setup using the model's documented key, or use UEFI Firmware Settings from Windows Advanced startup.
- Locate the Secure Boot settings. On applicable ASUS motherboards, select Windows UEFI mode as OS Type. Notebook firmware may instead show a direct Secure Boot Control setting.
- Use the normal standard key configuration for a standard Windows installation. Restore default Secure Boot keys only if the model's procedure requires it and you understand any custom-key or multiboot requirements.
- Save the changes and restart. Do not use a Clear Keys option as a way of enabling Secure Boot.
Secure Boot requires an appropriate UEFI startup configuration. If CSM must be disabled, first confirm that Windows and essential expansion hardware support the resulting configuration.
Verify in Windows and handle a failed startup
Reopen msinfo32 after Windows starts and confirm Secure Boot State is On. A firmware menu set to Windows UEFI mode does not by itself prove that all required keys and conditions are in place.
If Windows requests a BitLocker recovery key, use the saved key and investigate the configuration change. Do not clear the TPM to bypass the prompt.
If the PC no longer boots, return to firmware and restore the specific settings you recorded before the change. Do not repeatedly convert disks or reset all firmware options. For a boot-signature warning, verify that the installed operating system and recovery media are supported and properly signed.
Finally, check the other Windows 11 requirements separately. Secure Boot does not add TPM 2.0, change the processor's compatibility, or increase storage capacity.
Related Articles
- TPM Initialization in Windows 11
Handle the security processor separately from Secure Boot. - Prepare a GPT System Disk
Check the conversion and UEFI prerequisites before changing boot mode.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- File synchronize
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Disk Master Help
- Windows Deleted File and Disk Recovery Tutorials
- Windows File and Data Recovery Tutorials
- More Windows Tutorials for Install, Security, Files, and PC Tips
- Windows Boot, Repair, and Recovery Environment Tutorials
- Windows Backup Tutorials
- Windows Restore Tutorials
- Windows Clone and Migration Tutorials
- Windows Server Backup, Recovery, and Management Tutorials
- Windows Disk, Partition, and Storage Management Tutorials