TPM Could Not Be Initialized in Windows 11: Safe Troubleshooting
The message TPM could not be initialized concerns the security processor used for features such as BitLocker and Windows Hello. It may come from firmware before Windows loads or from a Windows security component. Record where it appears, because the repair path depends on that distinction.
Do not clear or disable the TPM as a first experiment. Encryption and sign-in credentials may depend on it.
Protect recovery information before changing security settings
- Check whether BitLocker or Device Encryption is enabled. Retrieve the recovery key from its saved location, Microsoft account, or your organization's administrator.
- Confirm that you can access that key from another device. A copy stored only on the encrypted PC will not help if the PC stops unlocking.
- Make sure you know the account password, not just the Windows Hello PIN. A TPM reset may require Hello credentials to be set up again.
- For a managed work computer, contact the administrator before altering TPM ownership, firmware, or encryption policy.
A file backup and an encryption recovery key serve different purposes. One does not replace the other.
Read the TPM status in Windows
- Press Windows + R, enter
tpm.msc, and read the status and specification version. - Open Windows Security > Device security > Security processor details if available. Record any error rather than immediately clearing the device.
- Restart once and check again. If TPM is reported as ready, investigate whether the remaining problem is limited to Windows Hello or a particular application.
- If no compatible TPM is found, inspect the model's firmware documentation. Intel PTT and AMD fTPM are examples of firmware TPM implementations; do not switch between TPM devices without understanding existing key use.
TPM initialization is not normally repaired by disabling Windows Defender Firewall. Keep protection enabled and troubleshoot the component that is actually reporting the error.
Check firmware and updates for the exact model
Record the model and BIOS version from msinfo32. Review the manufacturer's support instructions for TPM-related updates. Install only the firmware intended for that exact device and hardware revision.
- Before an approved firmware update, save work, connect reliable power, and follow the manufacturer's BitLocker suspension instructions.
- Open firmware settings using the documented startup key or UEFI Firmware Settings in Advanced startup.
- Confirm that the expected security processor is enabled. Do not clear ownership, erase keys, or load unrelated defaults simply to make the menu look like another model.
- Complete the supported update procedure, restart, and check
tpm.mscagain. Confirm encryption protection has resumed.
If the error began after a firmware update, consult the vendor's specific recovery instructions. Firmware downgrade support varies and should not be assumed.
When clearing the TPM may be justified
Clear the TPM only after protecting recovery credentials and confirming that this is the documented remedy for the remaining problem. Microsoft's TPM troubleshooting guidance explains the consequences and the Windows clearing route.
On a supported unmanaged PC, the route may be Windows Security > Device security > Security processor details > Security processor troubleshooting > Clear TPM. Read the warning and follow the restart prompts. Clearing removes TPM-held keys; it is not equivalent to deleting ordinary files. Reconfigure affected sign-in features afterward.
If the TPM remains absent or fails vendor diagnostics, seek model-specific hardware support instead of repeating the reset.
Back up readable data before security maintenance
While Windows is accessible, Qiling Disk Master can protect selected files before firmware maintenance. Store the image on another drive and keep the encryption recovery key separately.
Step 1. Connect the backup drive and open File backup.
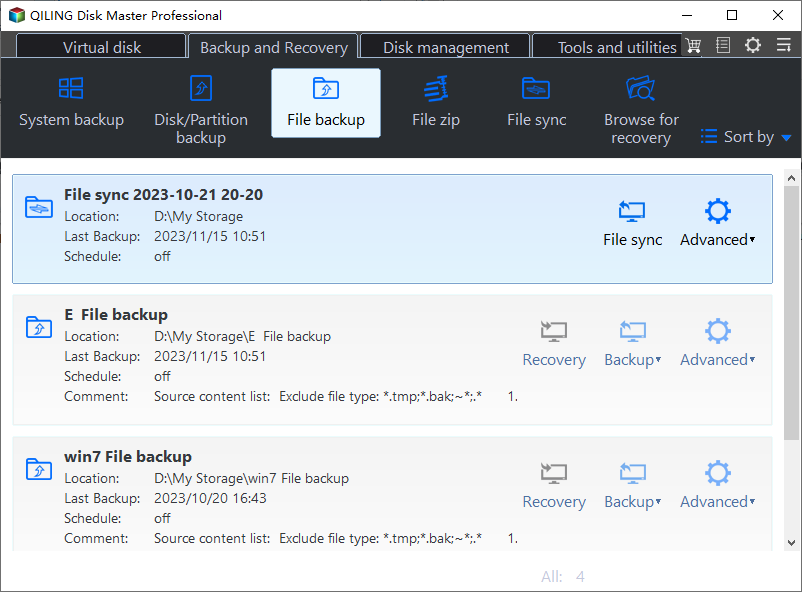
Step 2. Select required folders directly in the tree control. Include current work files and exports of application settings you may need later.
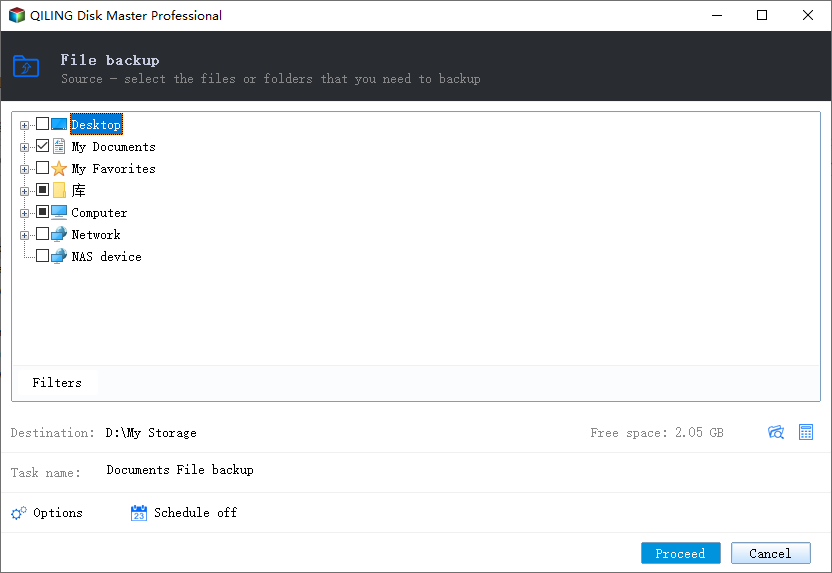
Step 3. Choose the external destination, review the task, and click Proceed. Verify a sample restore, then disconnect the backup drive before firmware work.
Related Articles
- Find a Windows 11 BitLocker Recovery Key
Prepare the key before changing firmware or security-processor settings. - Understand BitLocker Recovery
Separate encrypted-drive access from ordinary data recovery.
Products
Articles & Tutorials
- Data Recovery
- Data Backup
- File Recovery
- File Backup
- File synchronize
- System Backup and Restore
- Disk and Partition Clone
- Technical articles
- Disk Master Help
- Windows Deleted File and Disk Recovery Tutorials
- Windows File and Data Recovery Tutorials
- More Windows Tutorials for Install, Security, Files, and PC Tips
- Windows Boot, Repair, and Recovery Environment Tutorials
- Windows Backup Tutorials
- Windows Restore Tutorials
- Windows Clone and Migration Tutorials
- Windows Server Backup, Recovery, and Management Tutorials
- Windows Disk, Partition, and Storage Management Tutorials